Thanks!
If you liked this, we would love for you to share it with more people.



Healthcare cybersecurity is undergoing one of its biggest regulatory shifts in more than a decade. As ransomware attacks continue to disrupt hospitals, health systems, and health tech providers, regulators are raising expectations around how sensitive patient data is protected.
While existing HIPAA requirements remain in force, 2026 is an important year to watch as proposed changes to the HIPAA Security Rule aim to address today's increasingly complex healthcare technology environment, including cloud platforms, APIs, and interconnected systems.
For companies building healthcare software, understanding these changes early can help prevent costly compliance issues later.
HIPAA is a U.S. federal law enacted in 1996 to establish standards for protecting sensitive patient health information.
Although HIPAA contains several rules, organizations developing healthcare software typically focus on three primary areas:
And the requirements don't stop with healthcare providers. A software company can also have HIPAA obligations if it acts as a business associate when it creates, receives, maintains, or transmits PHI on behalf of a covered entity. Choosing a software development partner therefore involves more than evaluating technical skills. You also need to understand how the partner will handle PHI and what responsibilities each party assumes.
For companies building or modernizing healthcare software, the distinction can have major consequences. Compliance gaps discovered late in development can require architectural changes, delay deployment, increase development costs, or expose sensitive patient information to unnecessary risk.
For that reason, HIPAA requirements should be considered before development begins. A capable software development partner should be able to identify where PHI enters the system, how it moves through the application and connected services, who needs access to it, and what safeguards are required to protect it.
A common misconception is that HIPAA only applies to hospitals and clinics.
In reality, the healthcare technology ecosystem has expanded significantly, and many organizations indirectly handling healthcare information also fall within HIPAA's regulatory scope.
Organizations commonly subject to HIPAA requirements include:
Working with a covered entity? If your company performs services for a covered entity that involve creating, receiving, maintaining, or transmitting PHI, you may qualify as a business associate.
Healthcare has become one of the most targeted sectors for cyberattacks. According to the U.S. Department of Health and Human Services (HHS), reports of large healthcare data breaches increased by 102% between 2018 and 2023. During the same period, the number of individuals affected by these breaches increased by 1,002%. In 2023 alone, more than 167 million individuals were affected by large healthcare data breaches—the highest number ever recorded—highlighting the growing cybersecurity challenges facing the healthcare sector and reinforcing the need for stronger cybersecurity safeguards across healthcare organizations.
The risk is growing alongside healthcare's reliance on connected technologies. Patient data now moves across EHRs, cloud platforms, third-party services, APIs, and other connected systems, creating more potential points of exposure.
For companies building healthcare software, the takeaway is simple: security can no longer be treated as an isolated feature of the application. A vulnerability in one system, integration, or third-party service can expose sensitive patient data and create compliance problems across the wider environment.
Failure to comply with HIPAA can result in significant financial penalties and corrective actions imposed by the U.S. Department of Health and Human Services' Office for Civil Rights (OCR). Civil monetary penalties are determined based on factors such as the nature of the violation, the level of negligence involved, and whether the organization took reasonable steps to address the issue.
Beyond monetary fines, organizations may also be required to implement corrective action plans, undergo increased regulatory oversight, and strengthen their compliance programs following an investigation. Data breaches can also lead to reputational damage, contractual risks, operational disruption, and loss of customer trust, particularly for software vendors serving healthcare organizations.
For this reason, many organizations view HIPAA compliance not only as a regulatory obligation but also as a critical component of enterprise risk management and cybersecurity governance.
One of the most significant HIPAA developments heading into 2026 is the proposed update to the HIPAA Security Rule. The proposal aims to modernize HIPAA by strengthening cybersecurity requirements to better address today’s threat landscape, where cloud computing, SaaS platforms, AI-powered applications, APIs, and interconnected healthcare systems have become standard across the industry.
However, it is important to emphasize that these changes are proposed and have not yet been finalized.
Even so, the proposal provides a useful indication of the direction healthcare cybersecurity requirements may be heading. For healthcare leaders, it also creates an opportunity to assess whether current security practices are prepared for a more demanding regulatory environment.
One of the most significant proposals is the removal of many existing "addressable" implementation specifications by making several security requirements mandatory unless a documented exception applies. The proposal also places greater emphasis on security measures such as multi-factor authentication (MFA), encryption, vulnerability management, penetration testing, and network segmentation.
For healthcare organizations and software vendors, this means cybersecurity controls that were previously implemented based on organizational discretion may become baseline expectations. Organizations with less mature security programs may need to invest in additional technologies, security expertise, and compliance activities to meet future requirements.
The proposed rule would require organizations to maintain a comprehensive inventory of technology assets and identify where electronic protected health information (ePHI) is created, received, maintained, or transmitted.
As healthcare organizations adopt more cloud platforms, third-party applications, APIs, and connected medical technologies, maintaining visibility into systems handling ePHI becomes increasingly important. A well-maintained asset inventory also supports faster incident response, more effective risk assessments, and improved governance across complex IT environments.
The proposed rule strengthens expectations around risk analysis by requiring organizations to perform more comprehensive and ongoing assessments of cybersecurity risks. It also places greater emphasis on maintaining documentation that demonstrates security controls are implemented, reviewed, and updated over time.
Compliance therefore becomes increasingly tied to an organization's ability to continuously identify, prioritize, and address those risks rather than treating security as a periodic audit activity. Organizations should expect greater scrutiny of how risks are identified, prioritized, and addressed throughout the lifecycle of their systems.
The proposed updates reinforce the importance of operational resilience by expanding expectations for incident response, contingency planning, backup procedures, and disaster recovery testing. Rather than simply maintaining documented plans, organizations would be expected to regularly test these procedures to verify they remain effective during cybersecurity incidents.
For organizations delivering healthcare software or digital health services, stronger resilience practices can help minimize operational disruptions, reduce recovery times, and demonstrate preparedness during customer security reviews and regulatory assessments.
Healthcare organizations also depend on an increasingly broad network of external providers.
Business associates—including healthcare software vendors, cloud service providers, and managed service providers that create, receive, maintain, or transmit ePHI—are expected to play a more active role in maintaining HIPAA compliance. The proposed rule reinforces the need for stronger third-party risk management, documented security practices, and ongoing oversight of vendors handling sensitive healthcare information.
As a result, healthcare organizations may apply more rigorous vendor security assessments during procurement and contract renewals. Companies serving the healthcare industry should be prepared to demonstrate mature security controls, comprehensive documentation, and well-defined governance processes to satisfy customer compliance requirements.
The proposed HIPAA changes could raise the security expectations placed on healthcare software companies: simply saying that a product is secure may no longer be enough.
Healthcare organizations may require vendors to provide more evidence of how they protect ePHI, manage security risks, and respond to incidents. As security expectations become more stringent, companies may face deeper questions about how they manage access, vulnerabilities, third-party services, incident response, and sensitive data.
Third-party services also matter. If a product relies on cloud providers, APIs, or other vendors that handle ePHI, their security practices become part of the overall risk. Companies need to know which third parties have access to PHI and how that access is protected.
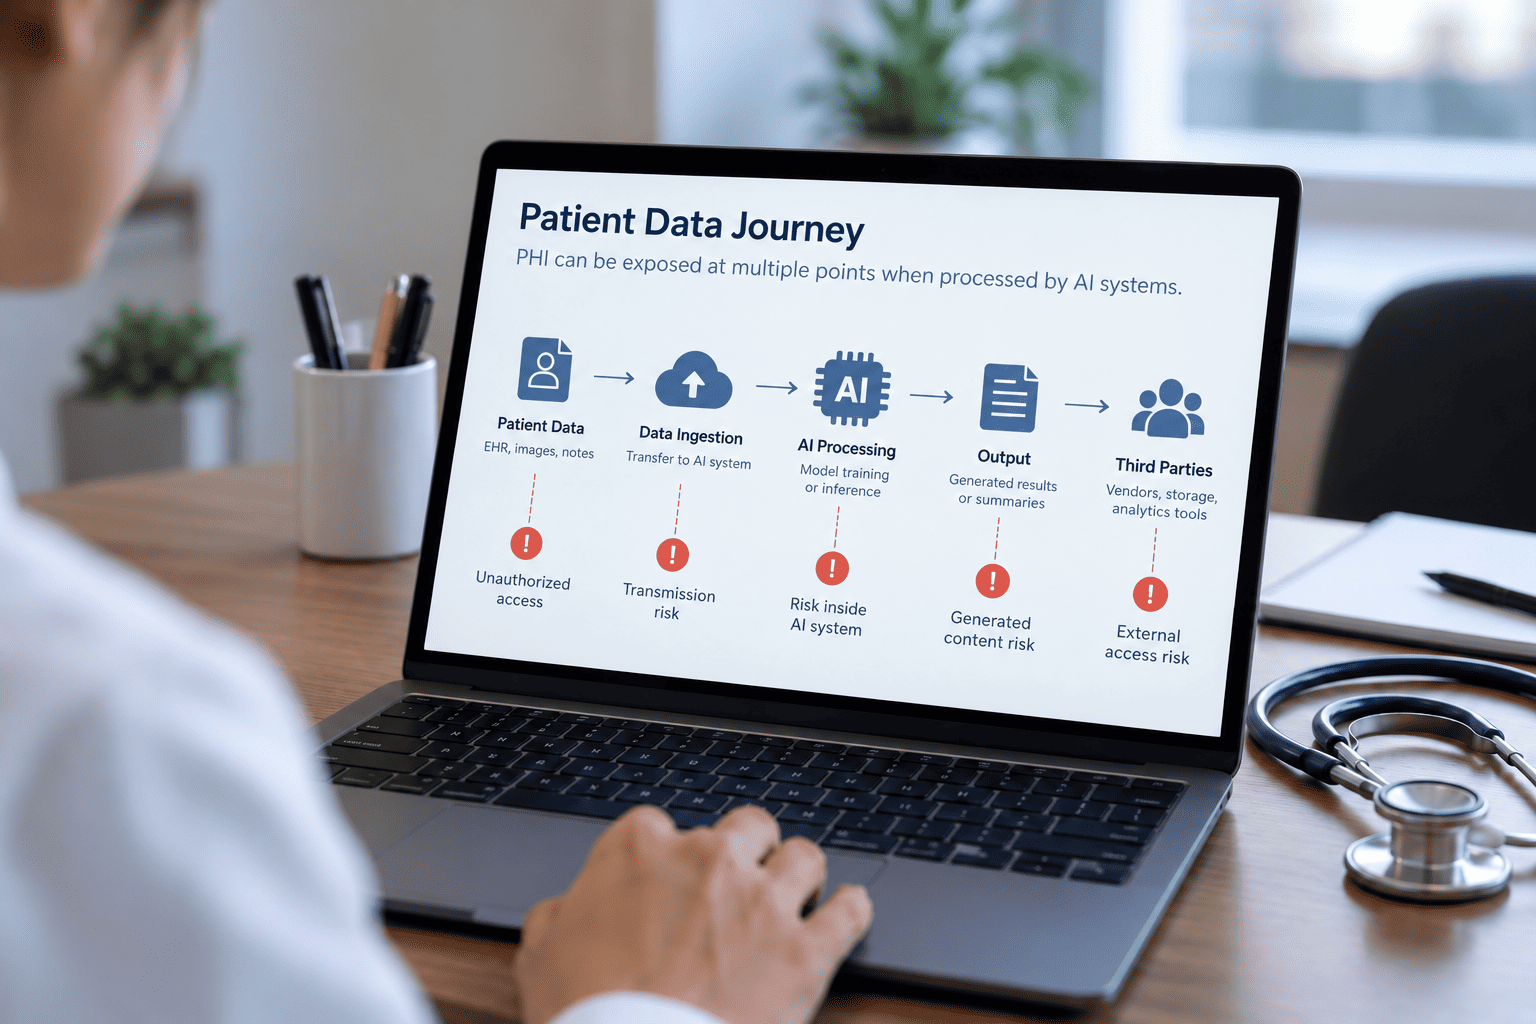
AI makes the question even more important.
When PHI passes through an AI system, the data may be exposed at several points—from inputs and inference workflows to application logs and external AI services. A company may therefore need to consider not only whether its own application protects PHI, but also what happens to that data once an AI service receives it.
The HIPAA Security Rule establishes the standards that covered entities and Business associates must follow to protect electronic protected health information (ePHI). Unlike the Privacy Rule, which focuses on how patient information may be used and disclosed, the Security Rule focuses on protecting ePHI from unauthorized access, alteration, loss, or disclosure.
The Security Rule organizes these requirements into three categories of safeguards: administrative, physical, and technical.
Administrative safeguards focus on how an organization manages security and risk. They include conducting regular risk assessments, establishing security policies and procedures, assigning security responsibilities, training employees, and maintaining incident response and contingency plans.
Physical safeguards protect the devices and facilities where ePHI is stored or accessed. Examples include controlling physical access, securing workstations and devices, and properly disposing of hardware that contains sensitive information.
Technical safeguards are where HIPAA requirements become part of the software itself.
HIPAA doesn't tell you which cloud provider, database, or security product to use. Instead, organizations need to choose safeguards that address the risks associated with their specific environment.
So what does that look like in practice?
Who can access patient data? Identity and Access Management (IAM) helps control user permissions, while Multi-Factor Authentication (MFA) adds another layer of protection if credentials are compromised.
What happens if sensitive data is intercepted or a system is compromised? Encryption helps protect ePHI both at rest and in transit, limiting the usefulness of exposed data.
Can you tell who accessed a patient's information? Audit logging and monitoring create a record of system activity that can help identify suspicious access and support investigations.
What happens when your application connects to another system? Secure API management helps protect data as it moves between applications and third-party services.
What happens when something goes wrong? Reliable backups and disaster recovery capabilities help organizations restore critical systems and data following an outage, security incident, or other disruption.
The right combination of safeguards depends on the risks, systems, and workflows involved. The goal isn't to collect as many security tools as possible. It's to ensure the technology, processes, and controls work together to protect the confidentiality, integrity, and availability of ePHI.
Many organizations mistakenly believe HIPAA compliance can be achieved simply by signing a Business Associate Agreement or using a HIPAA-eligible cloud provider.
But neither is enough.
A BAA establishes responsibilities between the parties, while a HIPAA-eligible cloud provider can offer compliant infrastructure. Neither, however, makes the application compliant on its own, as the security of ePHI still depends on the controls, processes, and third-party services surrounding the application.
Several common mistakes can leave gaps in those controls, even when the right agreements and infrastructure are in place.
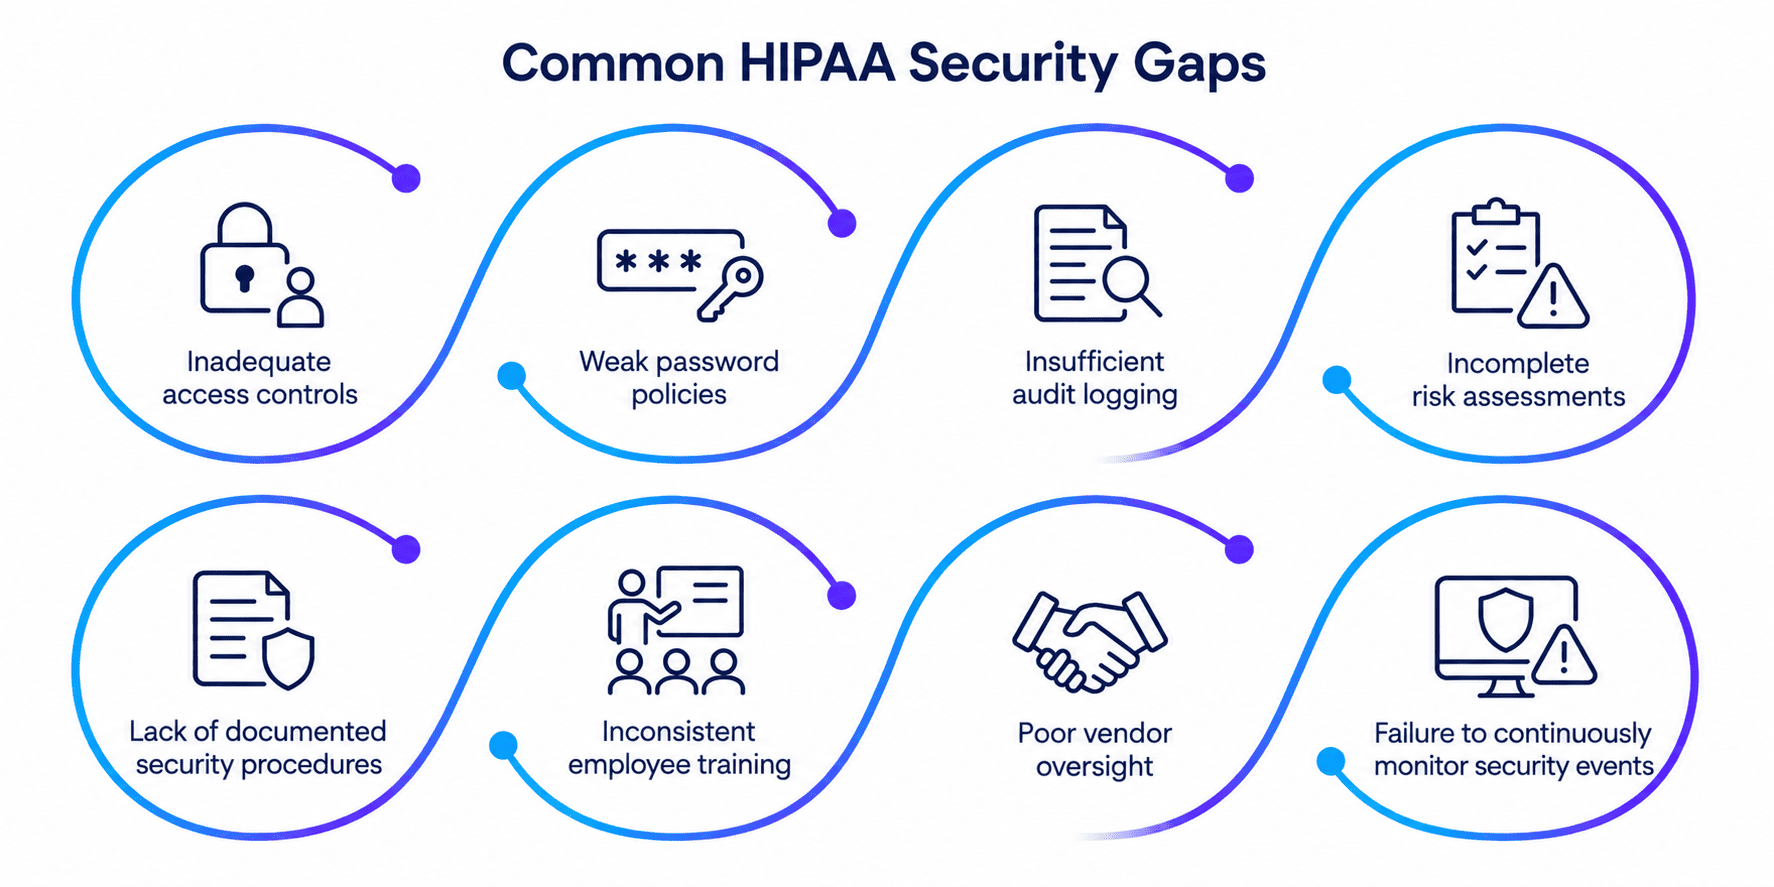
Preparing for a HIPAA audit requires more than maintaining documentation. Organizations should regularly evaluate whether their security controls remain effective and align with current regulatory expectations.
As a starting point, healthcare organizations and technology providers should ensure they can demonstrate the following:
Organizations that routinely review these areas are generally better positioned to demonstrate compliance, reduce cybersecurity risks, and respond effectively during regulatory audits or security incidents.
The proposed HIPAA Security Rule has not been finalized, but organizations don't need to wait for the final rule to identify potential gaps.
Start with your data. Where does your ePHI go?
Review every system, integration, cloud service, AI tool, and third-party vendor that handles ePHI. Confirm who has access, how the data is protected, and whether the appropriate agreements and safeguards are in place.
Pay particular attention to third-party services. A vendor or AI provider can introduce risk even when the underlying application is secure.
The proposed requirements may change, but the risks already exist. Finding a gap during development is far better than discovering it during an enterprise security review or after a breach.
For companies building or modernizing healthcare software, the immediate priority is simple: map your ePHI, identify everyone who touches it, and address the gaps before they become someone else's reason to reject your product.